Blogs

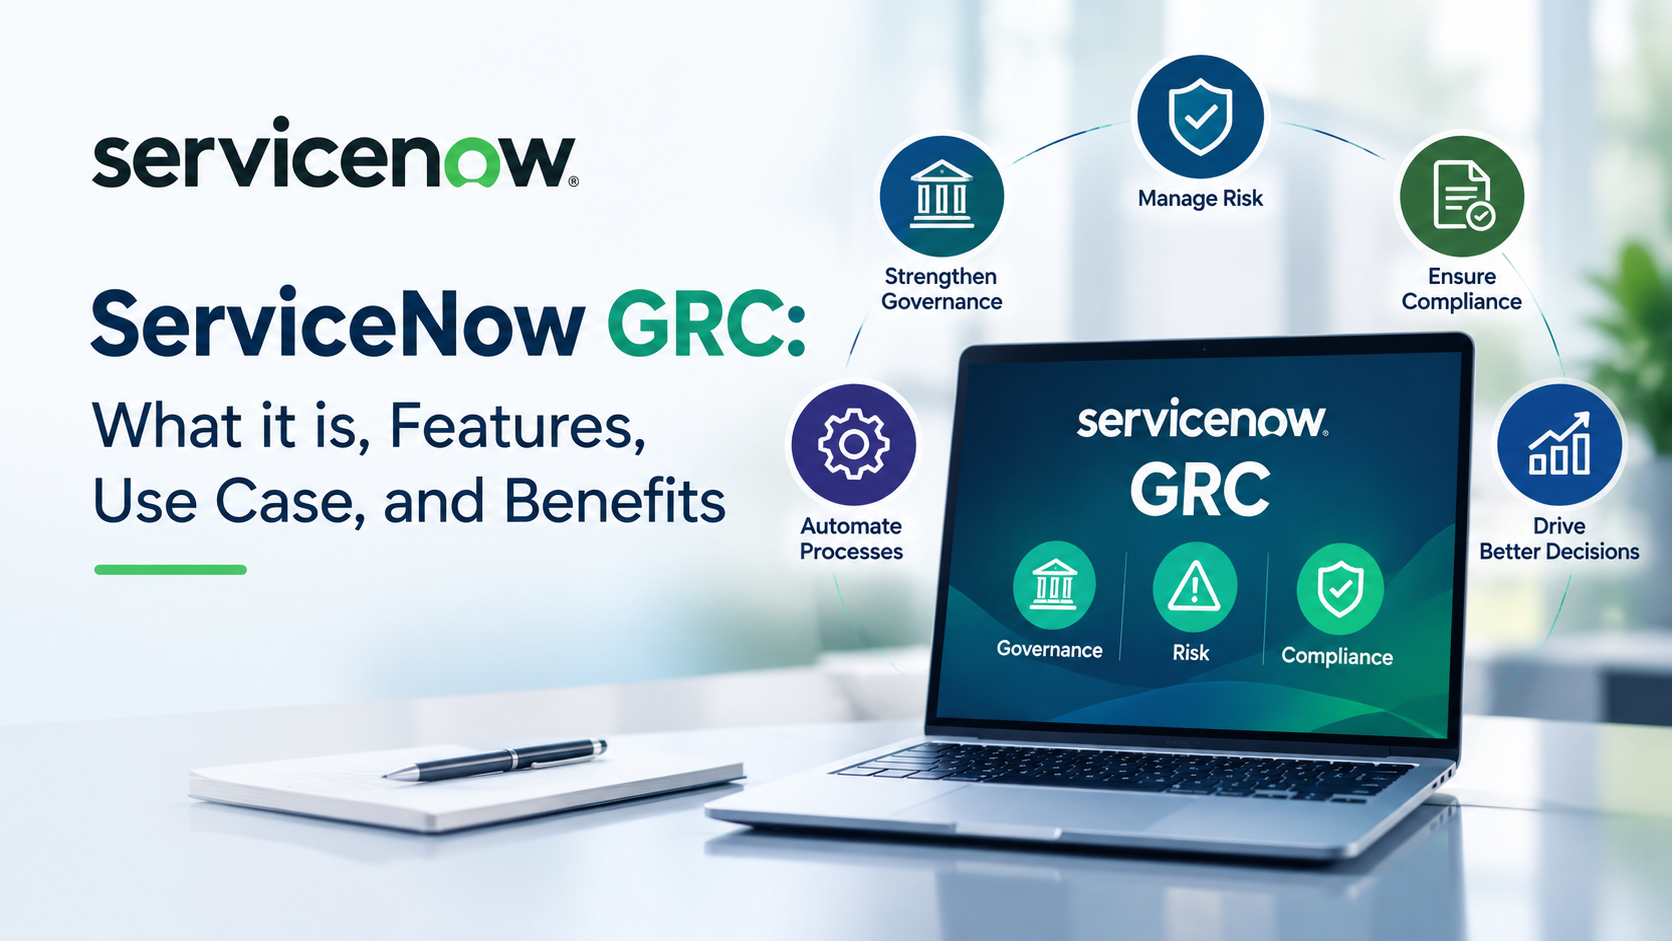
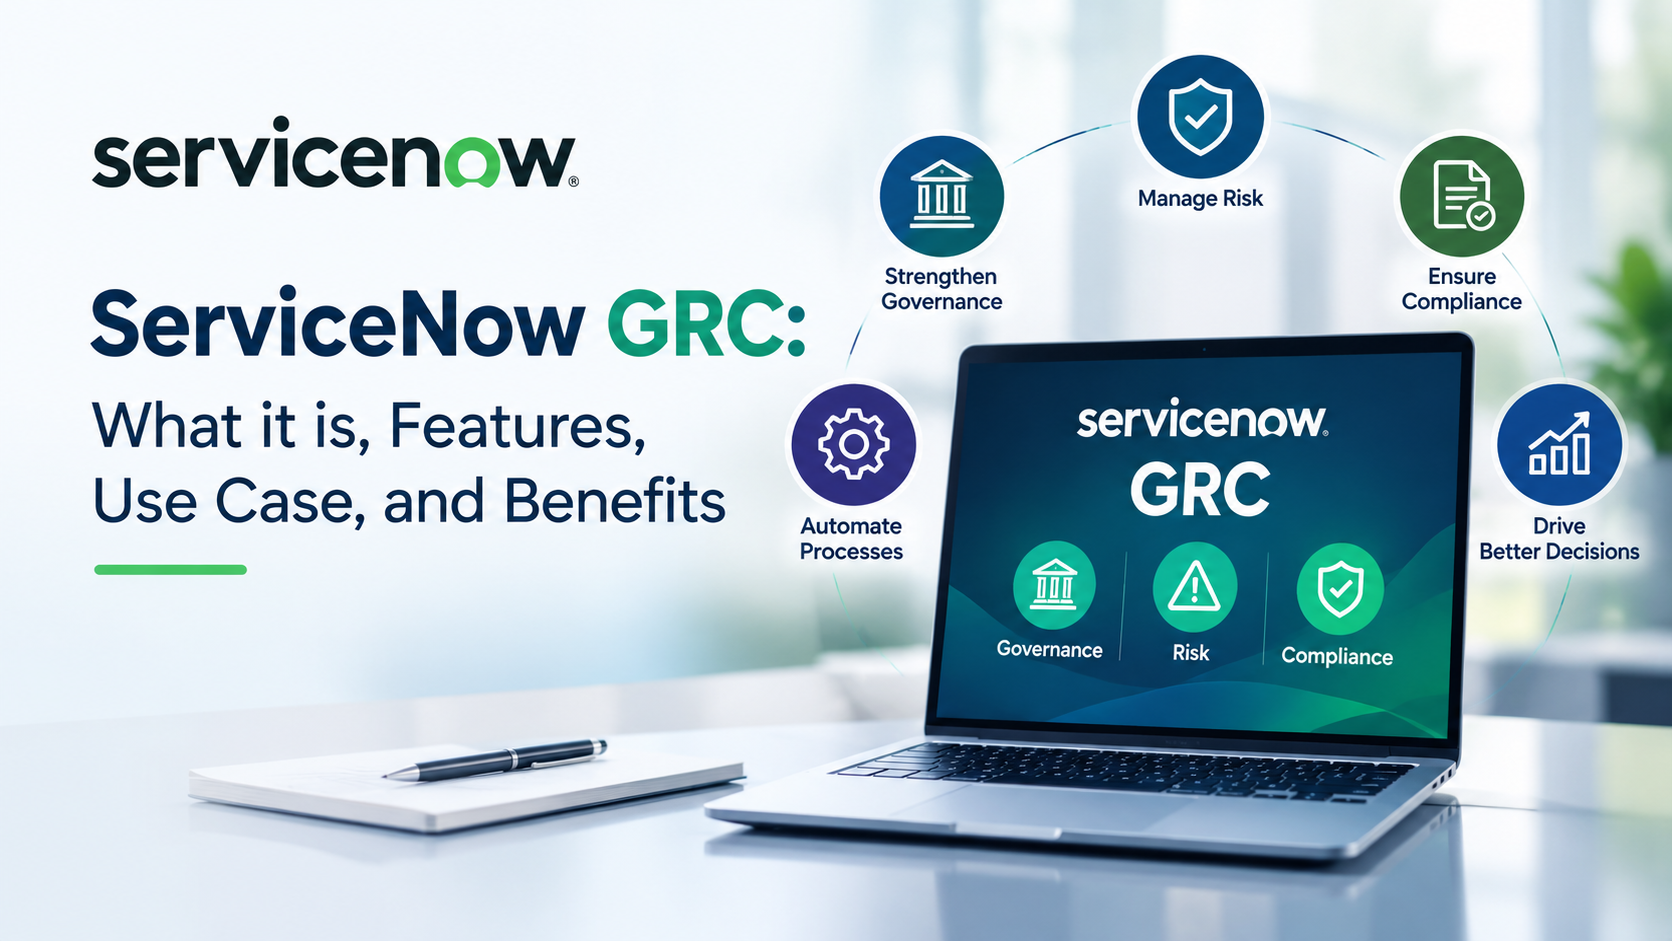
ServiceNow GRC: What it is, Features, Use Case, and Benefits

 1

To handle risk and maintain operational standards, businesses continue to manage their Governance, Risk, and Compliance. However, businesses using fragmented, manual systems often create bottlenecks that lead to more spreadsheets, email threads, evidence requests, and last-minute audit scrambles. The real challenge is rarely a lack of policies, and that is what ServiceNow GRC offers you.

As a key platform of ServiceNow, GRC is designed to improve governance, risk, and compliance activities by creating structured workflows. Instead of handling compliance as a periodic exercise, it helps organizations to manage policies, controls, risks, assessments, audits, and remediation through connected processes.

Let's see what ServiceNow GRC is, its features, use cases, and how it benefits businesses in the following review.


What is ServiceNow GRC


ServiceNow GRC is a platform built with governance, risk, and compliance capabilities that helps organizations manage policies, assess risks, monitor controls, conduct audits, and more.

The governance is built to establish policies, accountability, and business standards. Risk management helps your business identify, assess, monitor, and reduce potential risks. Whereas the compliance requirements can be mapped to a policy and related control, assigned to an accountable owner, tested through a defined workflow, and supported with evidence.

When a control fails, or a risk requires attention, teams can trigger the necessary action to fix it, rather than managing the issue via disconnected spreadsheets and email conversations.

Moreover, the platform helps develop a central control framework to manage all operations in one place. This way, it reduces duplicate compliance activities and makes control management easier to maintain.


Features of ServiceNow GRC 


Policy and Compliance Management 

Managing policies for a bigger organization can be difficult when considering all regulations, documents, approvals, ownership, and compliance requirements. ServiceNow GRC's Policy and Compliance Management provides a centralized structure for managing policies, controls, compliance requirements, and related documentation.

With this, organizations can connect policies, controls, and industry frameworks easily, enabling compliance teams to have better traceability over the organization's regulations. Moreover, policy owners can handle reviews, approvals, attestations, and updates under defined workflows.

Risk Management 

As the name suggests, Risk management helps businesses find potential risks, assess them, and mitigate them before they spiral out of control. ServiceNow Risk Management helps organizations assess risks, monitor risk indicators, identify issues, and provide remediation activities to the appropriate owners.

By replacing static registers, this structured management model helps teams find and easily sort every risk and provide a consistent view of risk exposure.

Audit Management 

To identify all resources and to make necessary audit preparation, organizations must locate evidence scattered across departments. With ServiceNow, Audit Management is made easier. It brings audit planning, control testing, findings, evidence, and follow-up activities into connected workflows.

By holding the existing risk and compliance data, auditors can support audit scoping and track findings through remediation. Thus, it reduces the need to repeatedly reconstruct evidence whenever an audit begins.

Third-Party Risk Management

Besides working on in-house solutions, every third-party vendor can introduce security, compliance, operational, and financial risks to an organization that are difficult to track. However, ServiceNow Third-Party Risk Management helps organizations assess vendors, manage risks throughout the relationship, and track remediation activities.

This creates greater visibility into third-party exposure across the vendor lifecycle.


Use Cases of ServiceNow GRC


Financial Services 

Banks and capital management firms always show higher priority to manage regulatory requirements, cybersecurity risks, audits, and third-party exposure. ServiceNow GRC helps streamline these operations by connecting every regulation with policies, controls, assessments, and remediation workflows. 

It allows teams to automate control testing, maintain audit evidence, track issues, and assign ownership. This way, it provides clear visibility over financial, operational, and technology risks, replacing manual spreadsheet checks.

Healthcare and Life Sciences

By handling sensitive patient data, privacy requirements, regulatory obligations, and complex vendor networks, Healthcare organizations are obligated to maintain GRC (Governance, Risk, Compliance). With ServiceNow GRC, Healthcare providers can manage policies, controls, assessments, evidence, and remediation easily under one connected workflow.

Moreover, internal departments can find compliance gaps, assign corrective actions, and maintain a structured audit trail for all departments.

Public Sector

Public sector agencies manage regulations, security controls, audits, vendors, and internal policies within their departments. By introducing ServiceNow GRC to their workflow, they can easily structure their workflows for control assessments, evidence collection, issue tracking, and remediation. It also benefits every team to evaluate regulatory changes and determine which policies or controls require updates. 

By helping with these activities, agencies can improve accountability and maintain better visibility into compliance obligations.


Benefits of ServiceNow GRC


Replacing Manual Compliance Work

When it comes to compliance and risk assessment, teams spend countless time in gathering evidence collection, approvals, and remediation using spreadsheets and email. With the introduction of ServiceNow GRC, businesses can easily automate these recurring events and structure workflow handoffs that enable teams to save time and focus on crucial tasks.

Better Visibility Into Risk 

Undergoing manual operations to assess and find risk information can be tedious and can be prone to error when it is delegated across teams. However, to fix this and streamline the process, ServiceNow brings relevant risk, control, issue, and compliance information together so stakeholders can work from a shared view.

Faster Audit Preparation

From assembling the team to preparing an audit can take weeks of time to complete and collect necessary evidence manually. However, with the help of ServiceNow, compliance activities and supporting records can be maintained within connected workflows, and organizations can make evidence easier to locate and maintain.

This can reduce the repetitive effort involved in preparing for internal and external audits.

Compliance Embedded Into Operations

By using GRC, its not about introducing another dashboard to your systems. It is about connecting compliance activities into your workflows that employees can benefit.

When risk assessments, control checks, approvals, issues, and remediation become part of operational processes, compliance is less likely to appear as a separate task that interrupts delivery. With ServiceNow, teams can work with defined checkpoints while maintaining visibility into risk and regulatory obligations.

By being a primary factor in streamlining and empowering old operational architecture, ServiceNow GRC proves its importance in an organization. By helping organizations connect compliance requirements, processes, controls, and workflows, it holds the responsibility for managing them.

For teams facing growing regulatory requirements, repeated audits, manual evidence collection, and limited risk visibility, ServiceNow GRC can make compliance more actionable and less disruptive.

At SGS Technologie, we help businesses streamline enterprise workflows and build workflow architecture that benefits all. By being a certified ServiceNow implementation partner, we have the capability to personalize and make your audits, governance, and compliance operation more easier.

To learn more about ServiceNow or for consulting, visit our webpage.
Category : ServiceNow

To handle risk and maintain operational standards, businesses continue to manage their Governance, Risk, and Compliance. However, businesses using fragmented, manual systems often create bottlenecks that lead to more spreadsheets, email threads, evidence requests, and last-minute audit scrambles. The real challenge is rarely a lack of policies, and that is what ServiceNow GRC offers you.

As a key platform of ServiceNow, GRC is designed to improve governance, risk, and compliance activities by creating structured workflows. Instead of handling compliance as a periodic exercise, it helps organizations to manage policies, controls, risks, assessments, audits, and remediation through connected processes.

Let's see what ServiceNow GRC is, its features, use cases, and how it benefits businesses in the following review.


What is ServiceNow GRC


ServiceNow GRC is a platform built with governance, risk, and compliance capabilities that helps organizations manage policies, assess risks, monitor controls, conduct audits, and more.

The governance is built to establish policies, accountability, and business standards. Risk management helps your business identify, assess, monitor, and reduce potential risks. Whereas the compliance requirements can be mapped to a policy and related control, assigned to an accountable owner, tested through a defined workflow, and supported with evidence.

When a control fails, or a risk requires attention, teams can trigger the necessary action to fix it, rather than managing the issue via disconnected spreadsheets and email conversations.

Moreover, the platform helps develop a central control framework to manage all operations in one place. This way, it reduces duplicate compliance activities and makes control management easier to maintain.


Features of ServiceNow GRC 


Policy and Compliance Management 

Managing policies for a bigger organization can be difficult when considering all regulations, documents, approvals, ownership, and compliance requirements. ServiceNow GRC's Policy and Compliance Management provides a centralized structure for managing policies, controls, compliance requirements, and related documentation.

With this, organizations can connect policies, controls, and industry frameworks easily, enabling compliance teams to have better traceability over the organization's regulations. Moreover, policy owners can handle reviews, approvals, attestations, and updates under defined workflows.

Risk Management 

As the name suggests, Risk management helps businesses find potential risks, assess them, and mitigate them before they spiral out of control. ServiceNow Risk Management helps organizations assess risks, monitor risk indicators, identify issues, and provide remediation activities to the appropriate owners.

By replacing static registers, this structured management model helps teams find and easily sort every risk and provide a consistent view of risk exposure.

Audit Management 

To identify all resources and to make necessary audit preparation, organizations must locate evidence scattered across departments. With ServiceNow, Audit Management is made easier. It brings audit planning, control testing, findings, evidence, and follow-up activities into connected workflows.

By holding the existing risk and compliance data, auditors can support audit scoping and track findings through remediation. Thus, it reduces the need to repeatedly reconstruct evidence whenever an audit begins.

Third-Party Risk Management

Besides working on in-house solutions, every third-party vendor can introduce security, compliance, operational, and financial risks to an organization that are difficult to track. However, ServiceNow Third-Party Risk Management helps organizations assess vendors, manage risks throughout the relationship, and track remediation activities.

This creates greater visibility into third-party exposure across the vendor lifecycle.


Use Cases of ServiceNow GRC


Financial Services 

Banks and capital management firms always show higher priority to manage regulatory requirements, cybersecurity risks, audits, and third-party exposure. ServiceNow GRC helps streamline these operations by connecting every regulation with policies, controls, assessments, and remediation workflows. 

It allows teams to automate control testing, maintain audit evidence, track issues, and assign ownership. This way, it provides clear visibility over financial, operational, and technology risks, replacing manual spreadsheet checks.

Healthcare and Life Sciences

By handling sensitive patient data, privacy requirements, regulatory obligations, and complex vendor networks, Healthcare organizations are obligated to maintain GRC (Governance, Risk, Compliance). With ServiceNow GRC, Healthcare providers can manage policies, controls, assessments, evidence, and remediation easily under one connected workflow.

Moreover, internal departments can find compliance gaps, assign corrective actions, and maintain a structured audit trail for all departments.

Public Sector

Public sector agencies manage regulations, security controls, audits, vendors, and internal policies within their departments. By introducing ServiceNow GRC to their workflow, they can easily structure their workflows for control assessments, evidence collection, issue tracking, and remediation. It also benefits every team to evaluate regulatory changes and determine which policies or controls require updates. 

By helping with these activities, agencies can improve accountability and maintain better visibility into compliance obligations.


Benefits of ServiceNow GRC


Replacing Manual Compliance Work

When it comes to compliance and risk assessment, teams spend countless time in gathering evidence collection, approvals, and remediation using spreadsheets and email. With the introduction of ServiceNow GRC, businesses can easily automate these recurring events and structure workflow handoffs that enable teams to save time and focus on crucial tasks.

Better Visibility Into Risk 

Undergoing manual operations to assess and find risk information can be tedious and can be prone to error when it is delegated across teams. However, to fix this and streamline the process, ServiceNow brings relevant risk, control, issue, and compliance information together so stakeholders can work from a shared view.

Faster Audit Preparation

From assembling the team to preparing an audit can take weeks of time to complete and collect necessary evidence manually. However, with the help of ServiceNow, compliance activities and supporting records can be maintained within connected workflows, and organizations can make evidence easier to locate and maintain.

This can reduce the repetitive effort involved in preparing for internal and external audits.

Compliance Embedded Into Operations

By using GRC, its not about introducing another dashboard to your systems. It is about connecting compliance activities into your workflows that employees can benefit.

When risk assessments, control checks, approvals, issues, and remediation become part of operational processes, compliance is less likely to appear as a separate task that interrupts delivery. With ServiceNow, teams can work with defined checkpoints while maintaining visibility into risk and regulatory obligations.

By being a primary factor in streamlining and empowering old operational architecture, ServiceNow GRC proves its importance in an organization. By helping organizations connect compliance requirements, processes, controls, and workflows, it holds the responsibility for managing them.

For teams facing growing regulatory requirements, repeated audits, manual evidence collection, and limited risk visibility, ServiceNow GRC can make compliance more actionable and less disruptive.

At SGS Technologie, we help businesses streamline enterprise workflows and build workflow architecture that benefits all. By being a certified ServiceNow implementation partner, we have the capability to personalize and make your audits, governance, and compliance operation more easier.

To learn more about ServiceNow or for consulting, visit our webpage.
Category
images
ServiceNow GRC Governance and Compliance